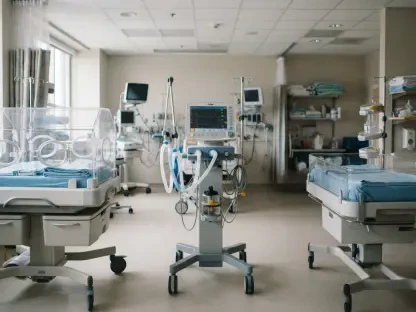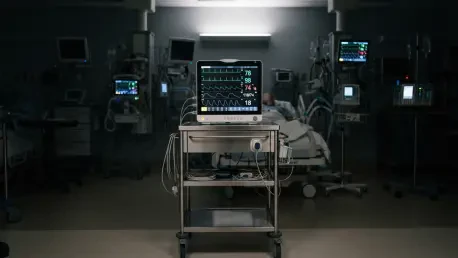
The transition to edge-based intelligence provides a robust solution for managing the high-velocity data streams generated by continuous vital sign monitoring equipment. In the high-stakes environment of the modern intensive care unit, the reliance on the Internet of Medical Things has reached a critical threshold where every heartbeat and respiratory rhythm is translated into a digital signal. While this interconnectivity facilitates immediate clinical intervention, it also opens a dangerous conduit for sophisticated cyber threats that target the data used to sustain life. Historically, hospitals relied on centralized cloud infrastructures for data processing, but the inherent latency and external exposure of these systems proved insufficient for current requirements. The emergence of a decentralized, dual-layer intelligence framework marks a significant departure from these outdated models. By locating advanced computational power directly at the ward level, healthcare providers ensure that data remains private.
Addressing the Vulnerabilities of the Digital ICU
Modern clinical settings operate within a paradox where the tools designed to save patients can simultaneously expose them to unprecedented risks from external actors. The proliferation of connected devices has expanded the attack surface of the hospital network, making it vulnerable to data interception, unauthorized access, and malicious telemetry injection. Because traditional security protocols often prioritize network uptime over data granularity, they frequently miss subtle manipulations that could lead to incorrect medical dosages or missed critical events. This technological gap necessitated a shift toward more integrated systems that recognize the interdependence of cybersecurity and clinical diagnostics. As the industry moves through the late 2020s, the focus has shifted from simple perimeter defense to an internal scrutiny of every data packet. Ensuring that monitoring equipment operates in a secure vacuum is no longer feasible; instead, intelligence must be embedded within the network fabric.
Adopting a Zero-Trust philosophy serves as the cornerstone of this new defensive posture, operating on the principle that no signal is inherently safe regardless of its origin. This approach is particularly vital in the intensive care unit, where the integrity of physiological data directly impacts survival rates and clinical outcomes. Relying on remote cloud servers for authentication introduces unacceptable delays, often measured in seconds, which can be the difference between life and death during a cardiac event. Furthermore, cloud dependency makes the hospital’s most sensitive equipment susceptible to broader internet outages or regional connectivity issues. By moving the verification process to a localized edge node, the system eliminates these external dependencies while providing a rigorous screening process. This localized control allows for a more granular inspection of data flows, ensuring that every piece of information entering the clinical pipeline is verified against known behavioral patterns.
The First Layer: A Soft-Voting Security Gatekeeper
The first line of defense in this sequential framework is a dedicated security module that functions as a strict gatekeeper for all incoming telemetry. This layer utilizes a soft-voting ensemble algorithm, which aggregates predictions from multiple machine learning models to achieve a consensus on the legitimacy of a network flow. Unlike traditional binary filters, this ensemble approach assesses the probability of a threat, allowing for a more nuanced and accurate detection of sophisticated intrusion attempts. By analyzing various characteristics of the data packets—such as arrival frequency, source identifiers, and payload size—the module identifies anomalies that deviate from the expected behavior of medical devices. This rigorous inspection occurs before the data reaches any diagnostic tools, creating a protective buffer that shields the clinical environment. The result is a highly resilient barrier that prevents malicious signals from compromising the patient monitoring system.
Operating at the edge of the network allows this security module to perform deep packet inspection without the bottlenecking typically associated with centralized traffic analysis. By processing information locally at the ward level, the framework maintains high throughput while identifying potential cyberattacks in real time. This immediate response is essential for blocking denial-of-service attacks or man-in-the-middle interventions that aim to disrupt the continuous stream of vital signs. Once a flow is identified as malicious, it is immediately quarantined, preventing it from propagating through the hospital’s internal infrastructure. Only traffic that is explicitly cleared as benign by the soft-voting mechanism is permitted to proceed to the next stage of the intelligence pipeline. This method ensures that the healthcare analytics layer remains unpolluted by noise or tampered information, providing a clean data set for the subsequent medical evaluation and reducing the overall computational burden.
The Second Layer: Diagnostic Precision via Gradient Boosting
Following the security screening, the verified data enters the healthcare intelligence layer, which is powered by a Histogram Gradient Boosting model. This specific algorithm was selected for its exceptional ability to handle the large, complex datasets typical of physiological monitoring in an intensive care setting. By organizing data into discrete bins or histograms, the model significantly accelerates the training process and improves the efficiency of real-time predictions without sacrificing accuracy. Its primary function is to analyze continuous streams of heart rate, oxygen saturation, and blood pressure to identify subtle patterns that indicate clinical deterioration. This proactive detection allows medical staff to intervene before a patient reaches a state of crisis, effectively moving the care model from reactive to preventive. The high precision of this layer ensures that even minor shifts in a patient’s condition are captured and flagged for immediate clinical review.
One of the primary challenges in the digital intensive care unit is the prevalence of alarm fatigue, often caused by frequent false positives from sensitive but inaccurate sensors. By placing the diagnostic layer behind a robust security gatekeeper, the framework significantly mitigates this issue by ensuring that the AI is only analyzing authentic physiological signals. Many false alarms are the result of signal interference or data manipulation, which the security layer identifies and removes before they can trigger a clinical alert. This sequential processing creates a high-fidelity environment where doctors can trust the alerts generated by the system, knowing they are based on untampered medical evidence. Furthermore, the Gradient Boosting model is fine-tuned to prioritize recall, ensuring that no genuine instance of patient instability is overlooked. This dual focus on security and sensitivity creates a reliable foundation for automated monitoring, allowing clinicians to focus their attention on the patients who need it most.
Validating Performance and Operational Efficiency
The effectiveness of this dual-layer architecture was validated through rigorous testing using industry-standard datasets that represent both cybersecurity and clinical monitoring. For the security component, the CICIDS-2017 dataset provided a comprehensive range of modern attack scenarios, against which the soft-voting ensemble achieved an impressive 99.4% accuracy. On the clinical side, researchers utilized the MIMIC-IV database, which contains de-identified health data from thousands of intensive care patients, to train and test the diagnostic module. The Histogram Gradient Boosting algorithm reached a cross-validated accuracy of 98.97%, demonstrating a near-perfect ability to identify critical health events. These results indicate that the system is not only capable of defending against external threats but also provides a level of diagnostic reliability that meets the strict requirements of a hospital. Such high performance across both domains suggests that the integrated approach is superior to siloed security or medical AI systems.
Operational efficiency is perhaps the most critical metric for any real-time medical application, as even the most accurate system is useless if it cannot provide timely insights. The end-to-end processing latency of the proposed framework was measured at approximately 28.8 milliseconds, a speed that comfortably exceeds the requirements for continuous vital sign monitoring. This rapid performance is achieved by eliminating the need for data to travel to a distant cloud server and back, instead keeping all computation within the local network infrastructure. By minimizing the time between data collection and clinical notification, the edge-based AI ensures that doctors have the most current information possible when making life-saving decisions. This low-latency threshold also allows the system to scale effectively across multiple patients in a busy ward without experiencing performance degradation. The combination of high accuracy and rapid response times marks a significant milestone in making dual-layer edge intelligence a practical reality for modern healthcare.
The Path Forward: Decentralized Healthcare Resilience
The success of this framework signals a broader trend toward edge intelligence, where the decentralization of AI creates more autonomous and resilient healthcare environments. By integrating security and diagnostics into a single, streamlined pipeline, hospitals can protect both the privacy of the patient and the integrity of the treatment. Looking ahead from 2026 to 2028, the evolution of this technology is expected to include even more sophisticated layers of data governance. Specifically, the integration of permissioned blockchain systems like Hyperledger Fabric could provide an immutable ledger for device logs and medical records. This would ensure that every action taken by the AI and every change in a patient’s status is permanently recorded and auditable, enhancing transparency and accountability within the clinical workflow. Decentralized storage solutions further complement this by providing a secure repository for high-resolution medical data that is resistant to single points of failure or centralized breaches.
The implementation of a dual-layer intelligence framework addressed the critical need for speed and security in the modern intensive care unit. Researchers identified the inherent flaws in cloud-reliant systems and established a localized alternative that protected the integrity of life-saving medical data. This transition to edge computing enabled clinicians to receive near-instantaneous alerts based on verified physiological signals, which fundamentally changed the response time to patient deterioration. By fusing network defense with clinical analytics, the system ensured that cyber threats were neutralized before they could impact patient safety or diagnosis. The study confirmed that high-level cybersecurity did not have to come at the expense of operational efficiency, as the low-latency processing supported real-time requirements. Ultimately, this approach provided a scalable blueprint for the next generation of medical technology, where the focus remained on securing the patient through decentralized and intelligent infrastructure.