Third-party due diligence has evolved from a one-time onboarding task into an ongoing process of verification and continuous compliance monitoring. This shift is critical as the healthcare landscape becomes increasingly defined by its digital architecture, where Personal Health Information serves as the essential fuel for clinical operations. As hospitals and clinics transition away from legacy paper-based systems toward fully integrated digital ecosystems, the protection of diagnostic records and financial data has moved from an IT footnote to a strategic necessity. The high density of sensitive information within these systems has created a lucrative target for global threat actors, forcing a fundamental rethink of how trust is maintained between patients and providers. By 2026, the focus has moved beyond mere encryption toward a comprehensive lifecycle management approach that treats data as both a vital asset and a significant liability if mishandled by any party.
Reshaping Defense Strategies for Clinical Environments
Responding to Escalating Cybersecurity Threat Profiles
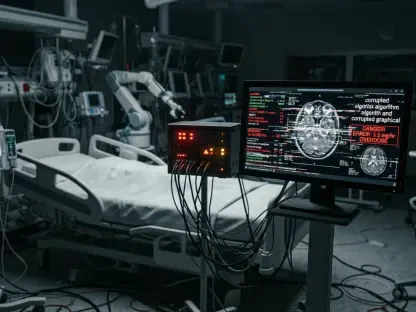
The threat profile for healthcare providers has intensified, with the sector now operating as the primary target for ransomware attacks that can cripple entire medical networks. This phenomenon is no longer categorized strictly as a technical challenge but is now recognized as a fundamental threat to patient safety and clinical outcomes. When a major medical facility loses access to its electronic health records, the consequences manifest as delayed treatments, canceled surgeries, and potential errors in critical medication dosages. Because the stakes involve human lives, the industry is adopting a clinical risk perspective, where cybersecurity is integrated into the emergency response protocols of the institution. Protecting the integrity of the network is seen as just as essential as maintaining the sterile environment of an operating room. Consequently, executives are moving away from passive firewalls toward dynamic defense systems that monitor clinical traffic in real-time.
Implementing Operational Preparedness and Resilience
To counter these sophisticated threats, regulatory bodies are now emphasizing operational preparedness rather than the simple existence of written policies. This shift demands that healthcare organizations demonstrate their resilience through tangible evidence of preparedness, such as regular tabletop exercises that simulate large-scale data breaches or system outages. Advanced techniques like network segmentation are becoming standard, ensuring that even if one segment of the infrastructure is compromised, the infection remains isolated and cannot spread to life-sustaining medical devices. Strict adherence to least-privilege access protocols further minimizes internal risks by ensuring that staff members can only view the specific data sets required for their immediate duties. Rapid detection capabilities are also being refined to identify dwell time where attackers linger in the system before triggering an event. These active measures create a robust shield for patient data.
Navigating Technological Advancements in Governance
Managing Third-Party Risks and Supply Chain Integrity
The growing reliance on external vendors for cloud hosting, billing, and telehealth services has introduced a dangerous misconception regarding the transfer of risk. Many healthcare organizations previously believed that outsourcing a specific business function also offloaded the legal and security responsibilities associated with the data handled by those partners. However, the current governance climate reinforces the principle that the primary provider remains ultimately responsible for any data mishandled by a third party. This reality has necessitated the implementation of rigorous, continuous due diligence frameworks that extend far beyond the initial contract signing. Organizations are now performing regular audits and security assessments of their entire supply chain to ensure that every link in the digital chain adheres to the same high standards. This rigorous oversight is essential for preventing supply chain attacks that exploit weaker vendors to reach the primary hub.
Navigating the Complexities of Artificial Intelligence
Artificial Intelligence is rapidly becoming a cornerstone of medical diagnostics and administrative efficiency, yet its data-hungry nature presents unique governance hurdles. To maintain compliance and patient trust, institutions are focusing on the principles of transparency and explainability within their AI models. This involves a deep understanding of exactly what data is being used to train these systems and how the algorithms arrive at their clinical conclusions. Governance teams must now verify a specific purpose of use for every data point processed by AI tools to avoid over-collection and unauthorized profiling. By integrating ethics boards into the technology procurement process, providers can ensure that innovation does not bypass privacy protections. As these tools become more autonomous, the need for human-in-the-loop oversight remains critical to ensuring that AI-driven decisions are both medically sound and fully compliant with existing laws and privacy standards.
Sustaining Strategic Resilience in Healthcare
The evolution of healthcare data governance reached a critical turning point where passive compliance was replaced by active, operational resilience. Organizations that successfully navigated this transition prioritized the integration of cybersecurity into their clinical workflows, ensuring that patient safety remained at the center of all digital initiatives. They implemented real-time monitoring and zero-trust architectures to handle the increased connectivity of modern medical platforms. Furthermore, successful leaders formalized their third-party oversight and established clear ethical guidelines for the deployment of artificial intelligence. By investing in continuous training and adopting a design-first approach to privacy, these institutions secured their infrastructure against increasingly sophisticated threats. The industry moved toward a model where data protection was recognized as a fundamental component of medical ethics, ensuring that the promise of digital health was delivered safely.