Small and micro-enterprises in the healthcare IT sector are largely exempt from the stricter cybersecurity requirements introduced by the European Union's NIS2 Directive. This regulatory carve-out creates a significant "blind spot" in Luxembourg, where the journey of sensitive patient data remains
When competitive tension is destroyed by a data leak, government officials often find that scrapping a multi-million dollar contract is the only legal remedy available. This reality became starkly apparent in Victoria during early 2026, when a high-stakes procurement process for orthopaedic
Third-party due diligence has evolved from a one-time onboarding task into an ongoing process of verification and continuous compliance monitoring. This shift is critical as the healthcare landscape becomes increasingly defined by its digital architecture, where Personal Health Information serves
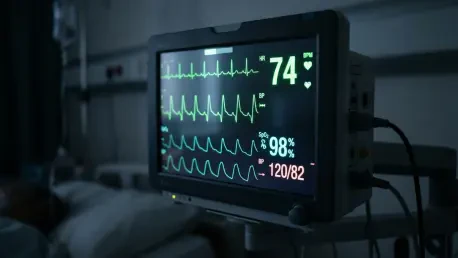
The shift toward end-to-end encryption in medical devices presents a new challenge for security frameworks that rely on inspecting raw biometric data to find anomalies. While the Internet of Medical Things (IoMT) has drastically improved patient outcomes by enabling real-time telemetry for devices
Ransomware recovery metrics have shifted focus from simple prevention to the speed at which a healthcare provider can restore critical services after an incident. This evolution reflects a growing realization that total immunity from digital intrusion is an unrealistic goal for complex medical
The sudden and total paralysis of critical healthcare infrastructure at the University of New Mexico Health Sciences Center illustrates how quickly digital vulnerabilities can transform into a public safety emergency in our current interconnected medical landscape. In late October, a sophisticated
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27